It’s Monday morning, your coffee’s still brewing, and suddenly your inbox blows up.
Not with sales leads or customer kudos - but with legal notices.
Turns out, your call center made a series of robocalls that violated federal rules.
Before lunchtime, regulators slap you with a fine large enough to sink your entire business.
Sound unlikely?
Tell that to those two Texas telemarketers fined a whopping $225 million for robocalls.
Ouch!
In 2025, call center compliance isn’t just legal jargon.
It’s your shield against lawsuits, customer distrust, and reputational wildfires.
The good news? Staying compliant doesn't have to be a headache.
Keep reading this below easy-to-follow compliance checklist guide to:
- Keep your call center thriving.
- Your customers are happy.
- And your business is out of hot water.
Let’s get started!
A. What exactly is call center compliance?
Call center compliance means following the rules that govern how you interact with customers and handle their data.
Think of it as a playbook for staying legal and ethical.
It covers:
- Consent: Getting permission to record calls or use customer info.
- Disclosures: Saying the right things, like “this call may be recorded.”
- Data Security: Protecting sensitive info like credit card numbers or health details.
- Regulations: Adhering to laws like TCPA, HIPAA, GDPR, or PCI-DSS.
Table 1 – Big-ticket rules & penalties
Regulation | Who It Covers | Must-Do | Max Civil Penalty* |
TCPA | Any outbound voice/SMS | Prior express consent, DNC, time-of-day | $1,500 per call |
HIPAA | Health info handlers | Protect PHI, minimum data | Up to $2.13 M per violation |
PCI DSS v4.0 | Anyone taking card data | Encrypt, mask, segregate | $500k+ plus bank fees |
FDCPA | Debt collectors | “Attempt to collect a debt” disclosure | $1,000 per violation |
GLBA | Financial orgs | Safeguards Rule, privacy notice | $100k per violation |
The stakes? One missed step can cost millions.
For example
HIPAA civil penalties run $141 to $2.13 million per violation, with fresh 2025 settlements topping $3 million.
B. 10-point call center compliance checklist
This checklist is your go-to guide for ensuring compliance in regulated industries like finance, healthcare, and collections.
Compliance focus | Key requirement / disclosure | Risk (if missed) | Recommended practice / tools |
Consent captured | Obtain and document explicit consent before recording, autodialing, or texting | Up to $1,500 per call/text (TCPA) | Agent opening script; IVR consent prompt |
Honor Do-Not-Call (DNC) lists | Scrub numbers against national & internal DNC before dialing | Up to $43,792 per call; reputational damage | Subscribe to national registry; auto-update internal list; agent number check |
Mandatory disclosures in script | Include industry-specific statements (e.g., debt-collection, investment risk) every time | Fines / lawsuits for misleading communication | Legal-approved scripts; regular updates |
Secure call-record storage | Encrypt, retain per policy, restrict access, auto-delete on expiry | Data-privacy fines; loss of trust | Encrypted servers; role-based access; retention scheduler |
Protect payment / personal data | Mask or redact PCI, HIPAA, GDPR sensitive info in recordings & logs | Breach settlements (e.g., $6.85 M) | Agent training; auto-PII redaction; secure payment gateway |
Regular compliance training | Onboard & quarterly refresh on TCPA, GDPR, etc. | Knowledge gaps → violations | Scenario-based workshops; quizzes; QA feedback loops |
QA with compliance scoring | Score every call for required statements & behaviors | Hidden risk if only sampled | Add compliance fields to scorecard |
Documented escalation policy | Escalate complaints or high-risk issues instantly | Mishandled issues → legal action | Written flow; agent coaching; track escalations in CRM |
Automated monitoring (Auto-QA) | 100 % call coverage for keywords & anomalies | Manual QA covers 1-5 % only | Real-time speech analytics |
Maintain audit trail | Log consent, data access, QA reviews, escalations | Cannot prove compliance during audit | Systems with immutable logs; store 2–3 yrs; easy export for regulators |
1. Consent is captured (every single time)
Always get documented consent - verbal or written - especially before recording calls or making automated calls.
For instance, TCPA compliance for call centers requires explicit consent before using autodialers or sending marketing texts.
One violation can cost up to $1,500 per call or text, which quickly adds up if your agents are dialing thousands of numbers.
Example
Agent: “This call may be recorded for quality purposes. Is that okay?”
Customer: “Yes.” That’s consent captured.
Why it matters:
Without consent, you’re breaking the law in many regions, which can lead to hefty fines or legal action. It also shows customers you respect their privacy, building trust.
How to do it:
- Train agents to include consent statements in their opening script.
- Use automated prompts to play consent disclaimers before the agent joins.
- Leverage call center compliance software like Enthu.AI to detect and flag calls missing consent statements.
2. DNC (Do Not Call) lists are honored
Respecting Do Not Call lists is non-negotiable.
Call centers must check numbers against national and internal DNC registries to avoid contacting opted-out customers.
Violations can cost up to $43,792 per call.
Example
Customer: “Don’t call me again.”
(Their number must be added to your internal DNC list immediately.)
Why it matters
Calling someone on a DNC list can annoy customers and lead to fines. It shows you’re not listening to their preferences, which hurts your reputation.
A 2024 case saw a telemarketing company fined $29 million for DNC violations.
How to do it:
- Subscribe to national DNC registries.
- Maintain an internal DNC list for customers who opt out.
- Train and coach agents to verify numbers before dialing.
3. Scripts include mandatory disclosures
Industry-specific disclosures, like “this is an attempt to collect a debt” for collections, must be part of every relevant call.
Example:
In finance, an agent might say, “Investments involve risk; past performance doesn’t guarantee future results.” Skipping this could lead to regulatory issues.
Why it matters:
Missing disclosures can result in fines or lawsuits.
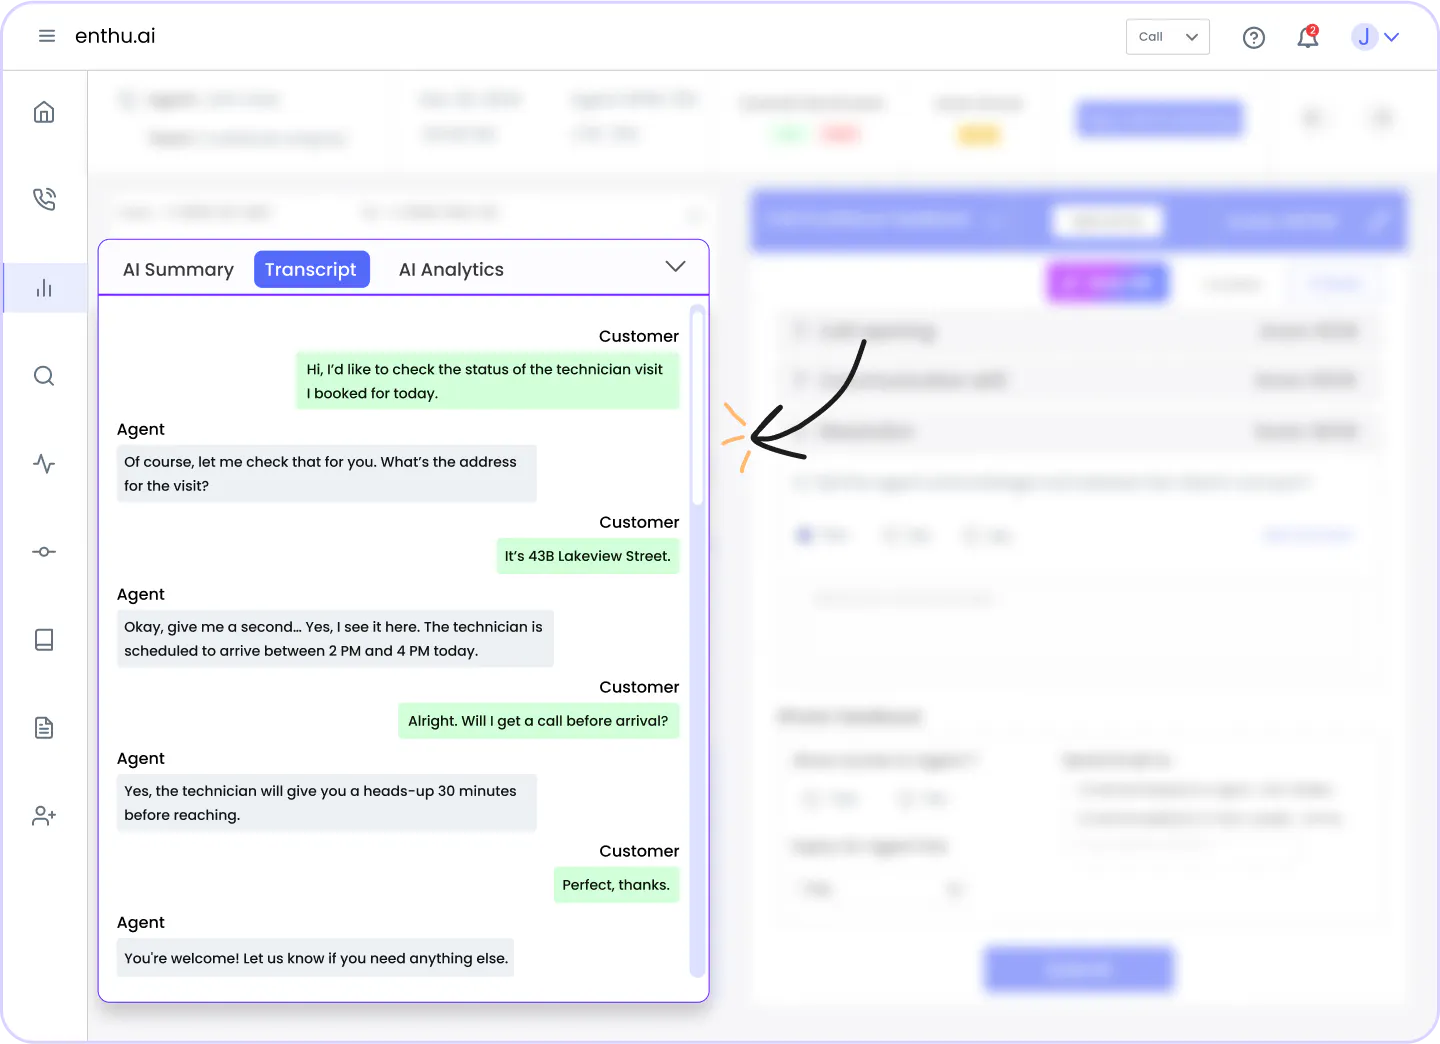
You can use call center software such as Enthu.AI that can scan transcripts to ensure these phrases are said, flagging omissions for review.
How to do it:
- Work with legal teams to craft compliant scripts.
- Update scripts regularly as regulations change.
- Use Enthu.AI to monitor script adherence.
4. Call recordings are stored securely
Recordings must be encrypted, stored per retention policies, and accessible only to authorized personnel.
Example:
A healthcare call center stores recordings with patient data securely to comply with HIPAA.
Why it matters:
Unsecured recordings can leak personal info, leading to fines and loss of trust. Secure storage shows customers you take their privacy seriously.
How to do it:
- Use encrypted servers for storage.
- Limit access to recordings.
- Auto-delete files after retention periods (e.g., GDPR requires specific timelines).
5. Payment and personal data are protected
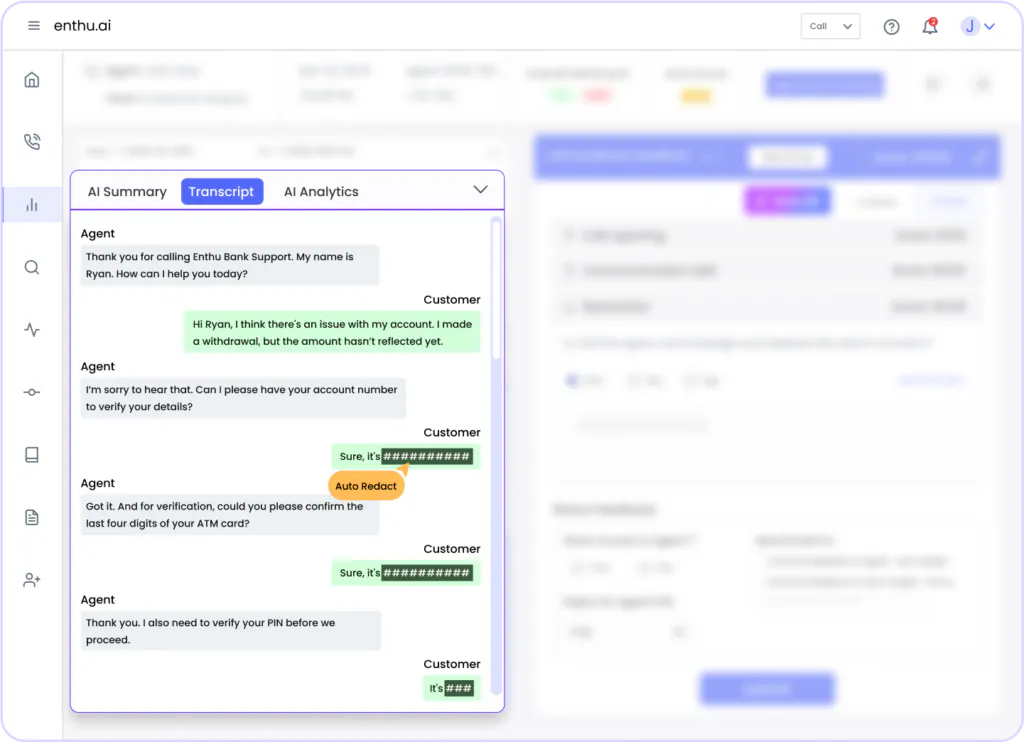
Sensitive data like credit card numbers or health info must comply with PCI-DSS or HIPAA compliance call center standards.
Example:
A customer shares their credit card number to make a payment. The system automatically masks the number in recordings and transcripts to keep it secure.”
Enthu.AI’s auto PII redaction feature automatically detects and removes sensitive data from recordings and transcripts.
Why it matters:
A 2020 data breach cost a health company $6.85 million.
How to do it:
- Train agents not to store sensitive data.
- Use auto-redaction tools to mask data.
- Ensure secure payment processes.
6. Training covers compliance regularly
Agents and QA teams need quarterly call center compliance training to stay updated on regulations like TCPA or GDPR.
Example:
During a training session, agents practice handling a customer’s GDPR data deletion request to ensure they follow the correct steps.
Why it matters
Outdated knowledge leads to accidental violations, which can be costly. Regular training using sales training software keeps everyone sharp and compliant.
How to Do It:
- Include compliance in onboarding.
- Run quarterly refreshers with real-world examples.
- Test agents with quizzes.
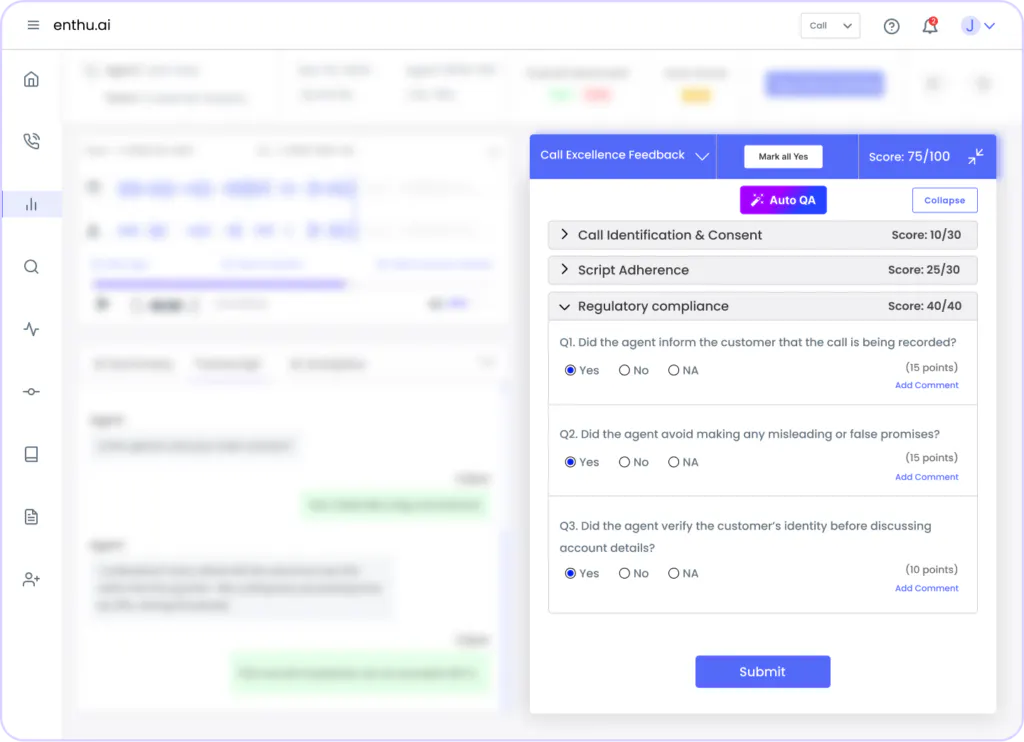
7. QA includes compliance scoring
Compliance should be part of every call audit, not just a side note.
Example:
A QA scorecard checks if agents said, “This call is recorded,” and scores compliance adherence.
Why it matters:
Without compliance scoring, you might miss risky behavior, leading to penalties. It ensures every call meets standards.
How to do it:
- Add compliance metrics to QA scorecards.
- Use call center quality assurance compliance for customizable scorecards.
8. Escalation policies are documented and followed
High-risk calls, like those with compliance issues, must be escalated promptly.
Example:
A customer raises a complaint about data misuse. The agent escalates the call to a supervisor, who logs it for review.
Why it matters:
Mishandling serious issues can escalate into legal trouble. Clear policies keep problems manageable and show professionalism.
How to do it:
- Document escalation procedures.
- Train agents on when to escalate.
- Monitor escalations for consistency.
9. Auto QA or monitoring tools are in place

Automated tools catch issues that manual reviews miss, covering 100% of calls.
Example:
An agent forgets to mention a required disclaimer. Enthu.AI’s system flags the call instantly for manager review.
Why it matters:
Manual reviews cover only 1-5% of calls, leaving gaps. Automation ensures nothing slips through, keeping you compliant.
How to do it:
- Implement tools for monitoring.
- Set alerts for compliance risks.
10. You maintain an audit trail
Every compliance action—consent, data access, reviews—must be logged for audits.
Example:
A regulator asks for proof of how a complaint was handled. Your system shows who accessed the call, when, and what was done.
Why it matters:
Without logs, you can’t prove compliance, risking fines. Audit trails show regulators you’re on top of things.
How to do it:
- Use tools with audit trail features.
- Store logs for 2-3 years.
- Ensure easy export for audits.
Checklist Point | Description | How Enthu.AI Helps |
Consent Is Captured | Document verbal/written consent for recordings | Flags missing consent statements |
DNC Lists Honored | Check numbers against DNC registries | Monitors compliance with DNC rules |
Mandatory Disclosures | Include industry-specific disclosures in scripts | Detects and flags missing disclosures |
Secure Recordings | Encrypt and limit access to recordings | Provides secure storage solutions |
Data Protection | Comply with PCI-DSS/HIPAA for sensitive data | Auto-redacts sensitive information |
Regular Training | Quarterly compliance training for agents | Supports training with call insights |
Compliance Scoring | Include compliance in QA scorecards | Customizable scorecards with metrics |
Escalation Policies | Document and follow escalation procedures | Flags high-risk calls for review |
Auto QA Tools | Use automation to monitor all calls | Analyzes 100% of calls in real-time |
Audit Trail | Log all compliance actions | Provides detailed, exportable logs |
C. Red flags: Signs you’re not fully compliant
Even with the best intentions, compliance gaps can sneak up on you.
These warning signs show your call center might be at risk of fines, lawsuits, or angry customers.
Spotting them early can save you a world of trouble.
1. Agents improvise instead of following scripts
Some agents think they can wing it, skipping required phrases like “this call may be recorded” or making promises they shouldn’t.
Why it’s a problem: Improvisation risks missing mandatory disclosures or using non-compliant language, which can trigger fines or legal action. It also makes it hard to ensure consistency across calls.
How to fix it: Train agents to stick to approved scripts. Use automated QA for call center compliance tools to monitor calls and flag when agents go off-script. Regular coaching can reinforce the importance of compliance.
2. Calls aren’t regularly reviewed
If you’re not checking calls often, you’re flying blind. Unreviewed calls can hide compliance issues like missing consent or improper data handling.
Why it’s a problem: Without regular reviews, small mistakes can pile up, leading to widespread non-compliance. You won’t know there’s an issue until it’s too late—like during an audit or lawsuit.
How to fix it: Set up a system to review calls consistently. Use call center solutions that can analyze 100% of calls, flagging risky ones for human review, so you catch problems early.
3. Sensitive info requested without security checks
Agents asking for credit card numbers or personal details without proper safeguards is a major red flag.
Why it’s a problem: Mishandling sensitive data violates laws like PCI-DSS or HIPAA, leading to fines and eroded customer trust. A single breach can devastate your reputation.
How to fix it: Train agents on secure data handling. Use tools like Enthu.AI to auto-redact sensitive info in recordings and transcripts, ensuring it’s protected.
4. QA audits cover less than 5% of calls
Relying on manual QA for a tiny fraction of calls leaves huge gaps in your compliance oversight.
Why it’s a problem: Low audit coverage means you’re gambling with compliance. Most issues go unnoticed, increasing your risk of fines or regulatory scrutiny.
How to fix it: Boost coverage with automated QA tools. These tools can review every call, catching issues like missing disclosures or risky phrases in seconds.
5. Can’t produce logs or recordings within 24 hours
If a regulator asks for call logs or recordings and you’re scrambling, you’re in trouble. Delays signal poor compliance management.
Example: A customer complains about a call, and regulators request the recording. Your team takes days to find it, raising red flags during an audit.
Why it’s a problem: Slow or missing records make it hard to prove compliance, risking penalties. It also suggests your systems aren’t audit-ready, which regulators hate.
How to fix it: Use tools with robust audit trails. This software logs every action—consent, access, reviews—and lets you export data quickly for audits.
Not sure where you stand?
Get 5 free call evaluation to spot compliance gaps. For more insights, check out this detailed compliance guide.
Conclusion
Call center compliance is a must for protecting your business and customers.
This 10-point checklist helps you stay ahead of regulations, avoid fines, and build trust.
Tools like Enthu.AI automate monitoring, redaction, and auditing, making compliance easier.
Don’t wait for a costly mistake—start implementing these practices today.
FAQs
1. What are the most common compliance issues in call centers?
Missing consent for recordings, ignoring DNC lists, skipping disclosures, insecure data handling, and outdated training are frequent pitfalls.
2. How can automated tools help with compliance?
Tools like Enthu.AI monitor all calls, flag violations, redact sensitive data, and provide audit trails, reducing errors and saving time.
3. What are the consequences of non-compliance?
Fines (up to $40,000 per violation), lawsuits, and reputational damage can hit hard, as seen in the $225 million FCC fine in 2021.
About the Author
Tushar Jain
Tushar Jain is the co-founder of Enthu.AI, a contact center intelligence software that helps teams automate quality assurance, coach agents and analyse customer interactions at scale. In the last 5 years, Tushar has personally overseen 100+ deployments of AI-driven analysis across sectors including lending, insurance broking, home improvements, lead gen agencies and real estate. Before founding Enthu.AI, Tushar led GTM at multiple consumer organisations where he first encountered the gap between call recording offered and and what managers actually needed to improve agent performance. Enthu.AI is currently rated 4.9/5 on G2 across 40+ verified reviews.